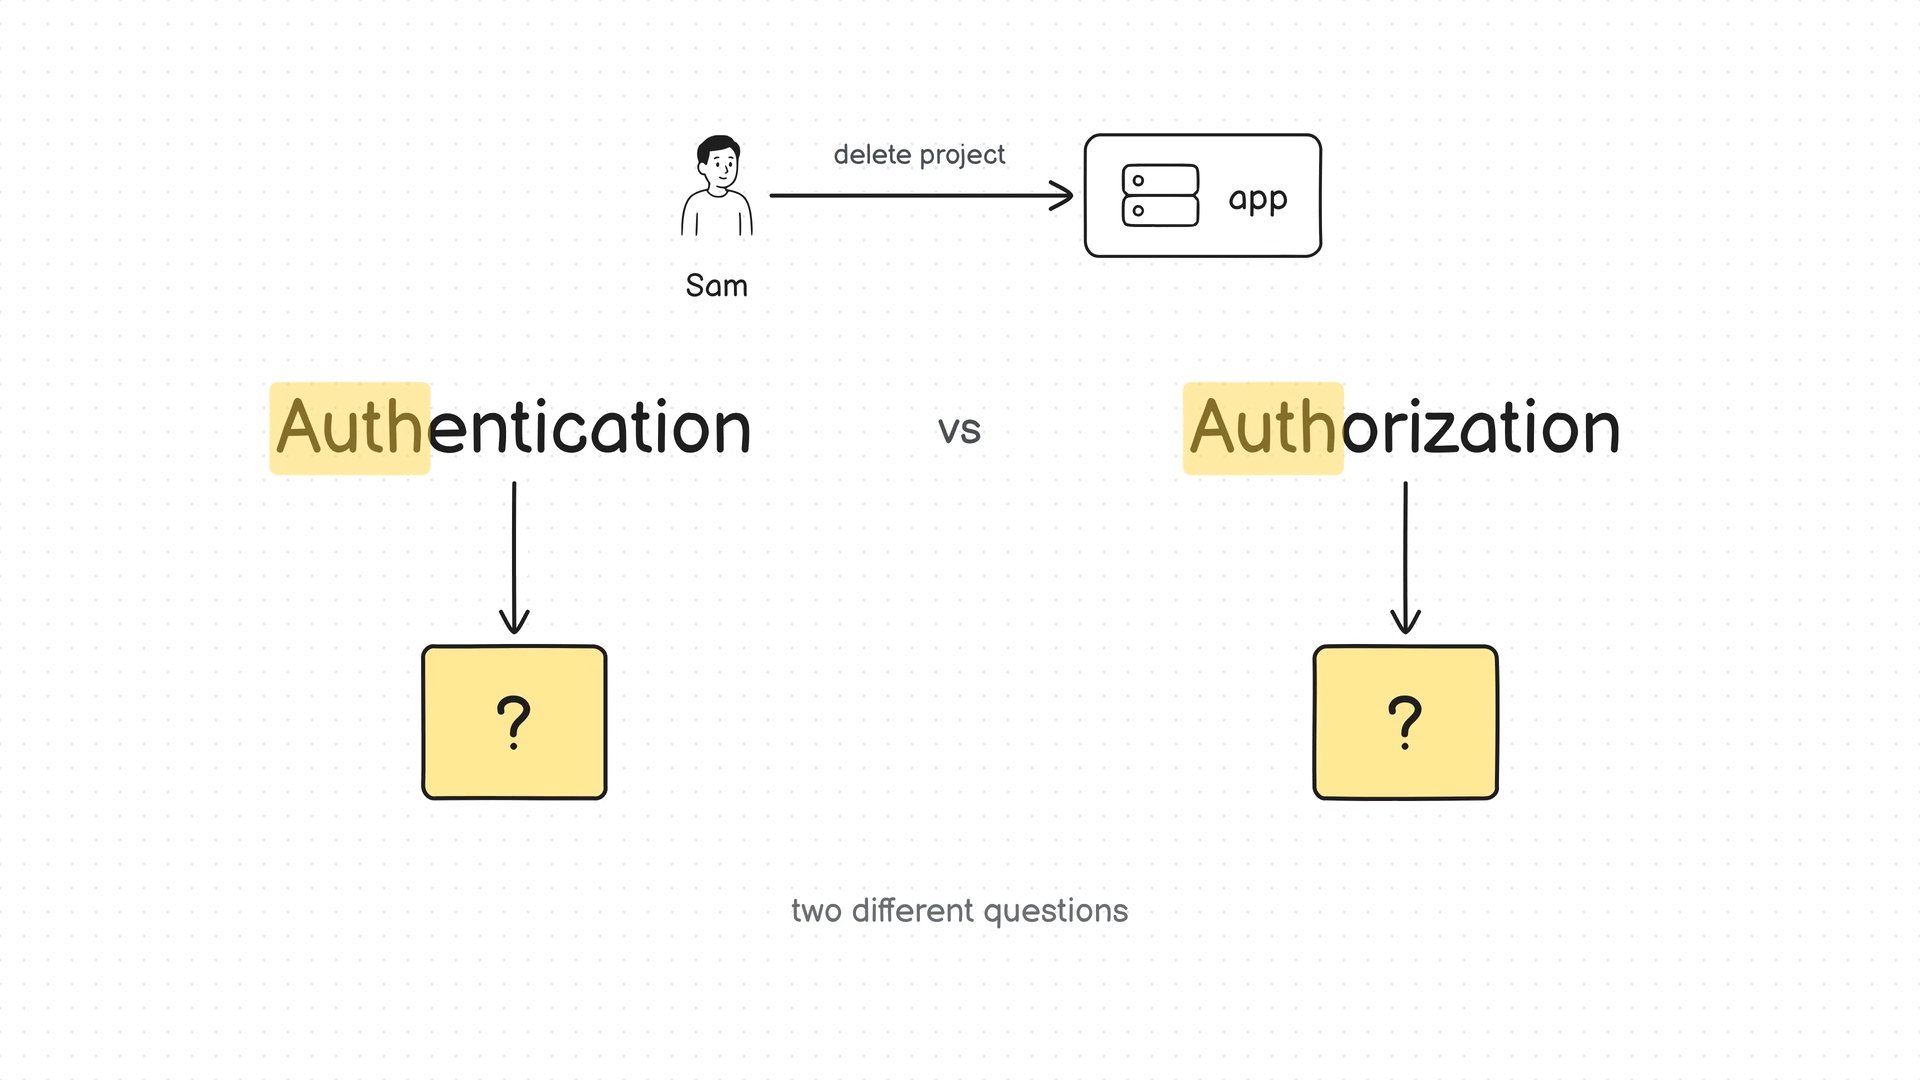
Authentication vs Authorization
Who you are vs what you can do, and when to return 401 or 403
What you'll learn
- What authentication is, and how sessions and tokens work
- What authorization is, with roles
- When to return 401 and when to return 403
- The 'change the ID in the URL' bug and how to prevent it
In this video, we'll look at how authentication checks who you are and how authorization decides what you're allowed to do. We'll cover passwords, passkeys, session cookies, JWTs, roles, and the difference between HTTP 401 and 403.
We'll also look at a common security mistake that lets users see someone else's data, and why checking that a user is logged in isn't enough.