Phishing and MFA
Why one-time codes can be phished, and how security keys stop it
What you'll learn
- How phishing pages steal passwords
- Why one-time codes can be phished
- How security keys and passkeys check the website for you
- Help desk checks and team habits that limit the damage
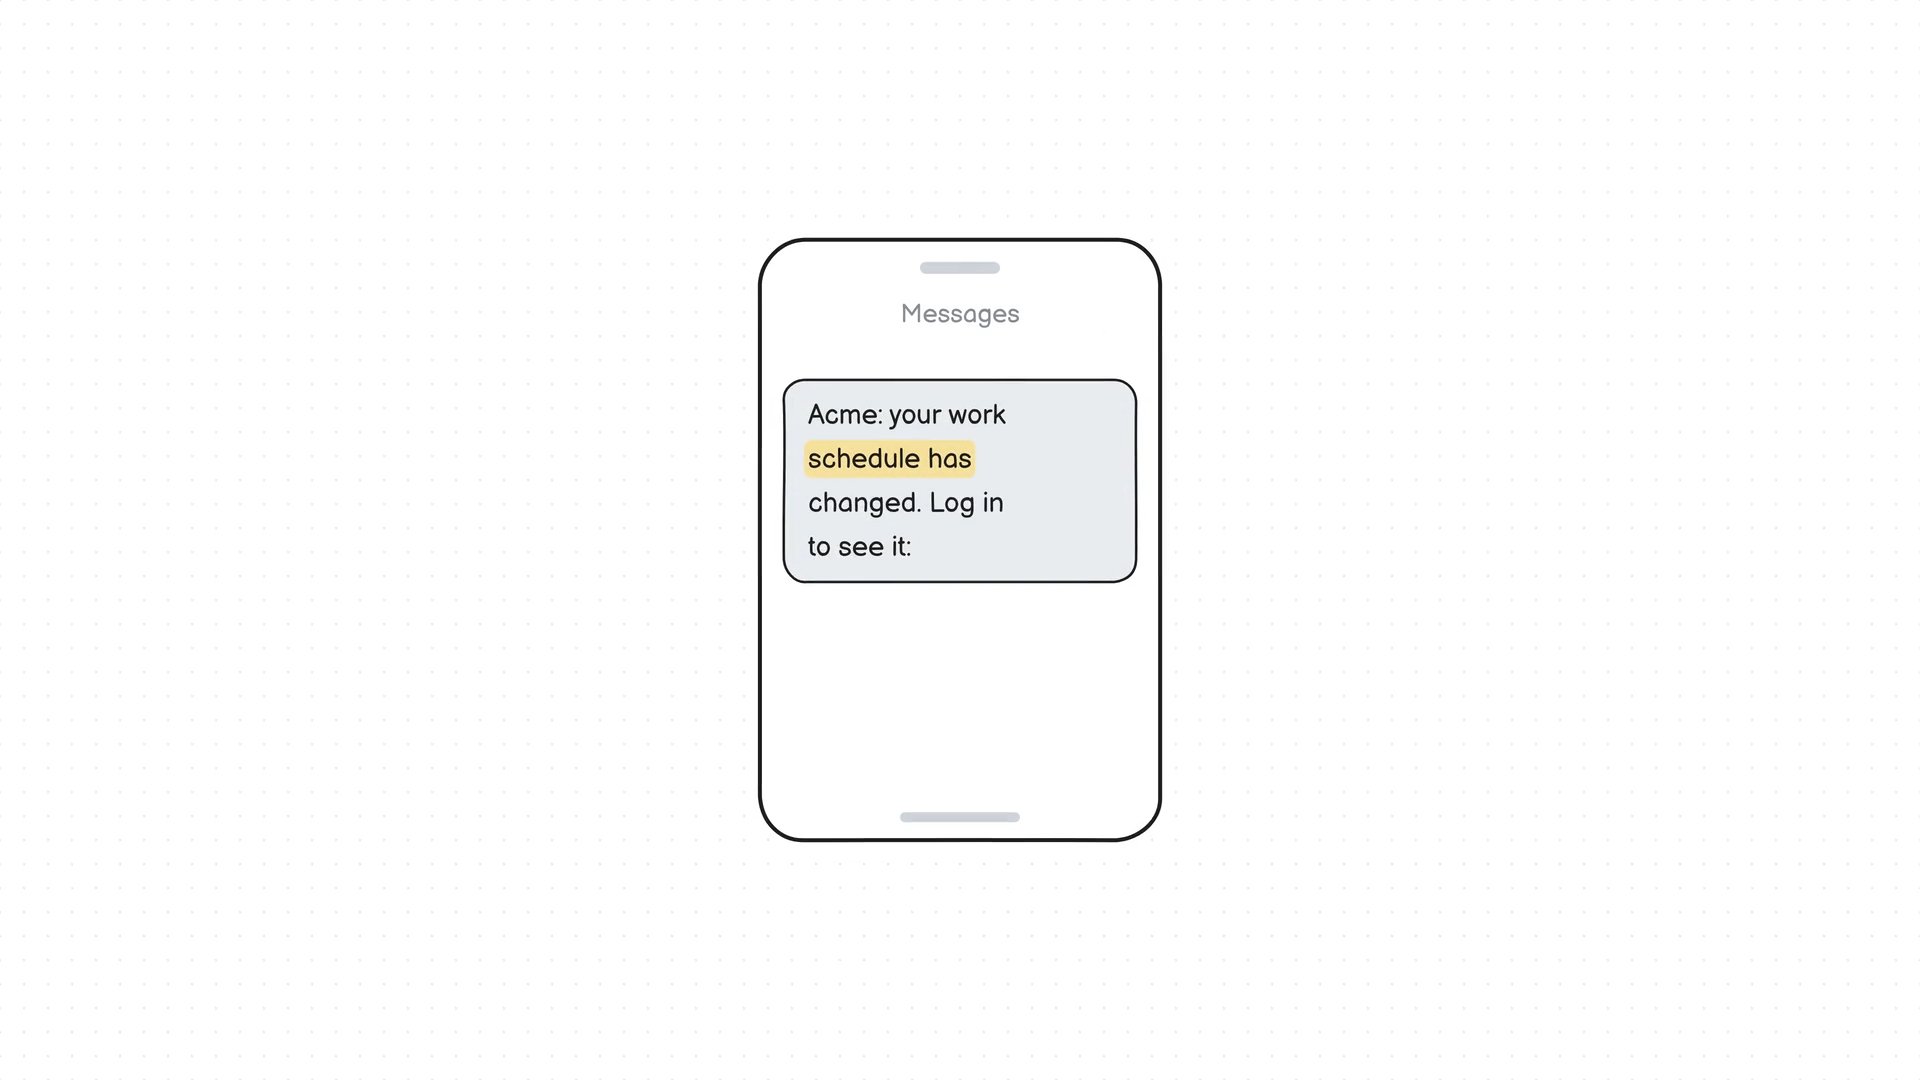
In this video, we'll look at how phishing works, starting with a text message that leads to a perfect copy of your company's login page. We'll cover the warning signs, and why sooner or later someone on every team will click.
We'll see why one-time codes can be relayed by a fake page, and how hardware security keys and passkeys check the website for you, so there's nothing to steal.
By the end, you'll know which kinds of MFA actually resist phishing, and what your team can do about it.