How SQL Injection Works
How one typed line can dump your whole database, and how parameterized queries stop it
What you'll learn
- How glued-together queries let input become code
- Why 1042 OR 1=1 returns every row
- Fixing it with parameterized queries
- Input checks and least-privilege database users
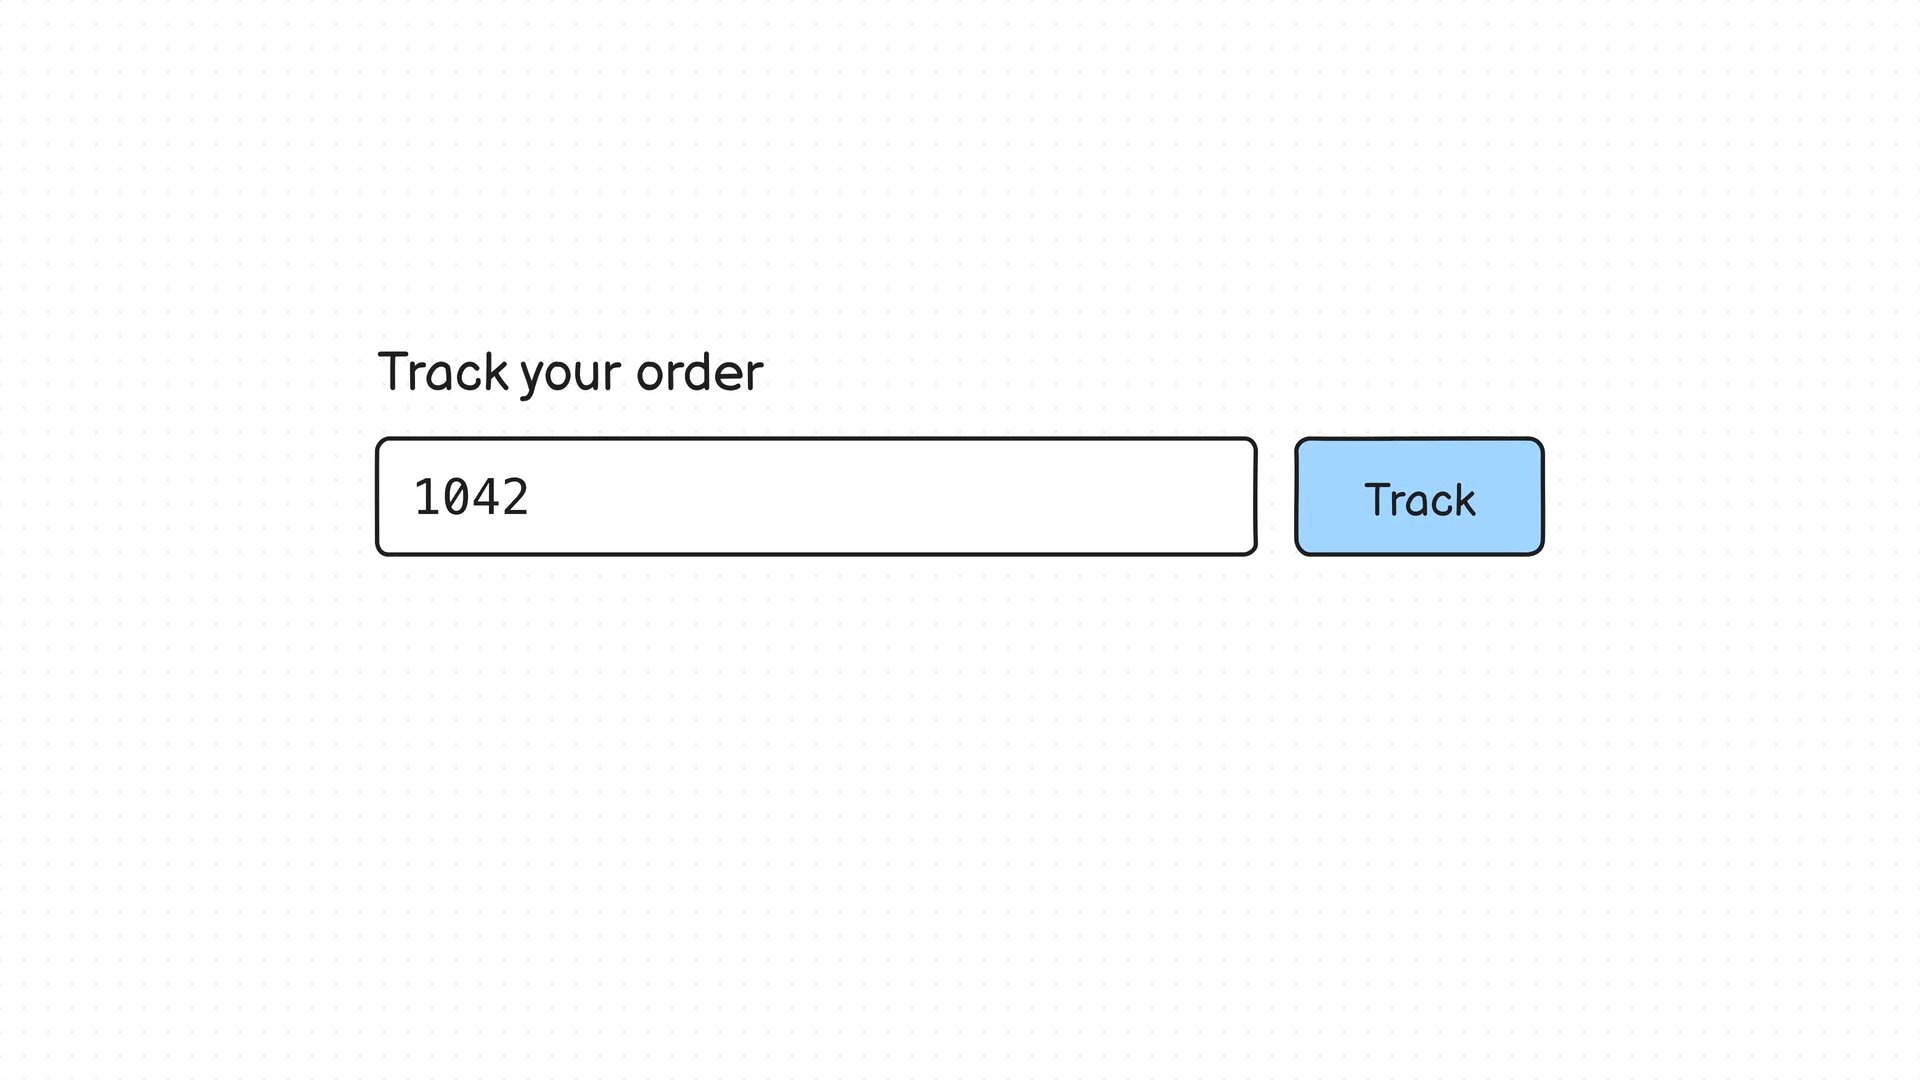
In this video, we'll look at how SQL injection works, using an order tracking page that builds its query by gluing strings together. We'll see how typing 1042 OR 1=1 turns one order into every order in the table, and why the database ends up reading the user's text as code.
Then we'll fix the bug with parameterized queries, where the query and the values travel separately. We'll finish with two extra habits: checking input and giving your app's database user only the access it needs.
By the end, you'll know how to spot an injectable query and how to write one that's safe.